

Image via [abc.net.au](https://www.abc.net.au/news/2026-10-30/actor-sir-patrick-stewart-dies-aged-86/107326458).
Sir Patrick Stewart, renowned British actor and star of 'Star Trek' and 'X-Men,' passed away at 86 after battling Alzheimer's disease and Lewy body dementia. His death was announced by his spokesperson Kelly Bush Novak through various media outlets including ABC News, CBS News, The Guardian, and Al Jazeera. Stewart is best known for playing Captain Jean-Luc Picard in Star Trek: The Next Generation and Professor Charles Xavier in the X-Men films. Fellow actors and friends paid tribute to him, with William Shatner calling him a
Sources: [abc.net.au](https://www.abc.net.au/news/2026-10-30/actor-sir-patrick-stewart-dies-aged-86/107326458) · [cbsnews.com](https://www.cbsnews.com/news/patrick-stewart-dies-age-86-star-trek-actor/) · [The Guardian](https://www.theguardian.com/culture/2026/oct/29/patrick-stewart-dead) · [aljazeera.com](https://www.aljazeera.com/editorial/2026/10/29/patrick-stewart-star-trek-captain-picard-and-x-men-actor-dies-at-86?traffic_source=rss) · [X / @WilliamShatner](https://x.com/WilliamShatner/status/2115902238921228332) · [X / @CBSNews](https://x.com/CBSNews/status/2115901834208371118)
North Korea launched around 10 short-range ballistic missiles toward the East Sea on Thursday, Oct. 29, South Korea's Joint Chiefs of Staff said. The missiles were fired from the Wonsan area on the North's east coast at about 12:30 p.m. local time (03:30 UTC) and flew roughly 250 kilometres, according to the JCS account cited by Reuters and Deutsche Welle. The exact missile models and the purpose of the launch have not been publicly identified. [Reuters](https://www.reuters.com/world/asia-pacific/north-korea-fires-projectile-toward-sea-off-east-coast-south-korea-military-says-2026-10-29/) | [DW](https://www.dw.com/en/north-korea-south-korea-japan-kim-jong-un-missile/a-79791900)
Seoul said it had strengthened surveillance and readiness for any further launches, while sharing information with the United States and Japan. Japan's Prime Minister's Office separately instructed agencies to gather and analyze information, keep the public informed, protect aircraft and vessels, and prepare for contingencies. Japan's Defense Ministry said the projectiles fell outside the country's exclusive economic zone, according to Yonhap as cited by DW. No damage or casualties have been reported in the coverage reviewed.
Why it matters: the launch adds to a tense period on the Korean Peninsula, where Seoul has recently proposed talks on border issues and Pyongyang has not accepted. The short-range missiles were directed toward waters off North Korea's east coast; the available reporting does not establish that they threatened Japanese territory. The next immediate step is continued monitoring by South Korean, U.S. and Japanese authorities. Further details about the missile type and North Korea's stated rationale remain unconfirmed.
~NorthKorea ~SouthKorea ~Japan ~WorldNews
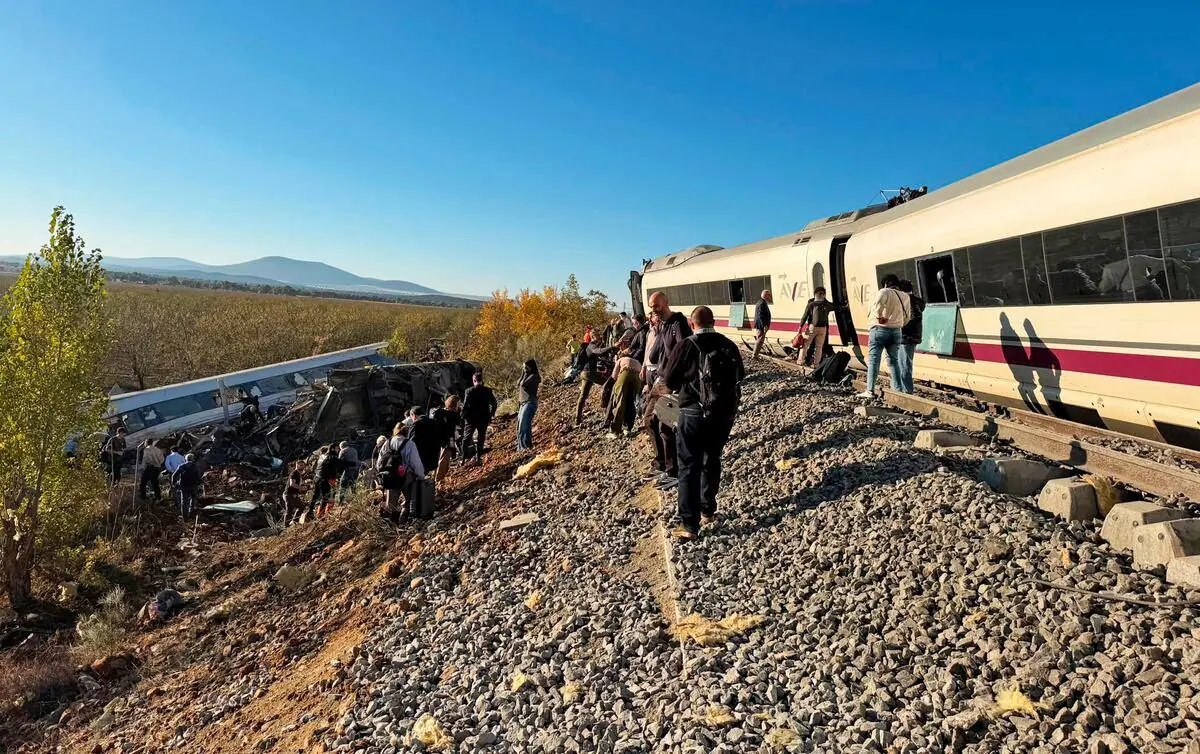
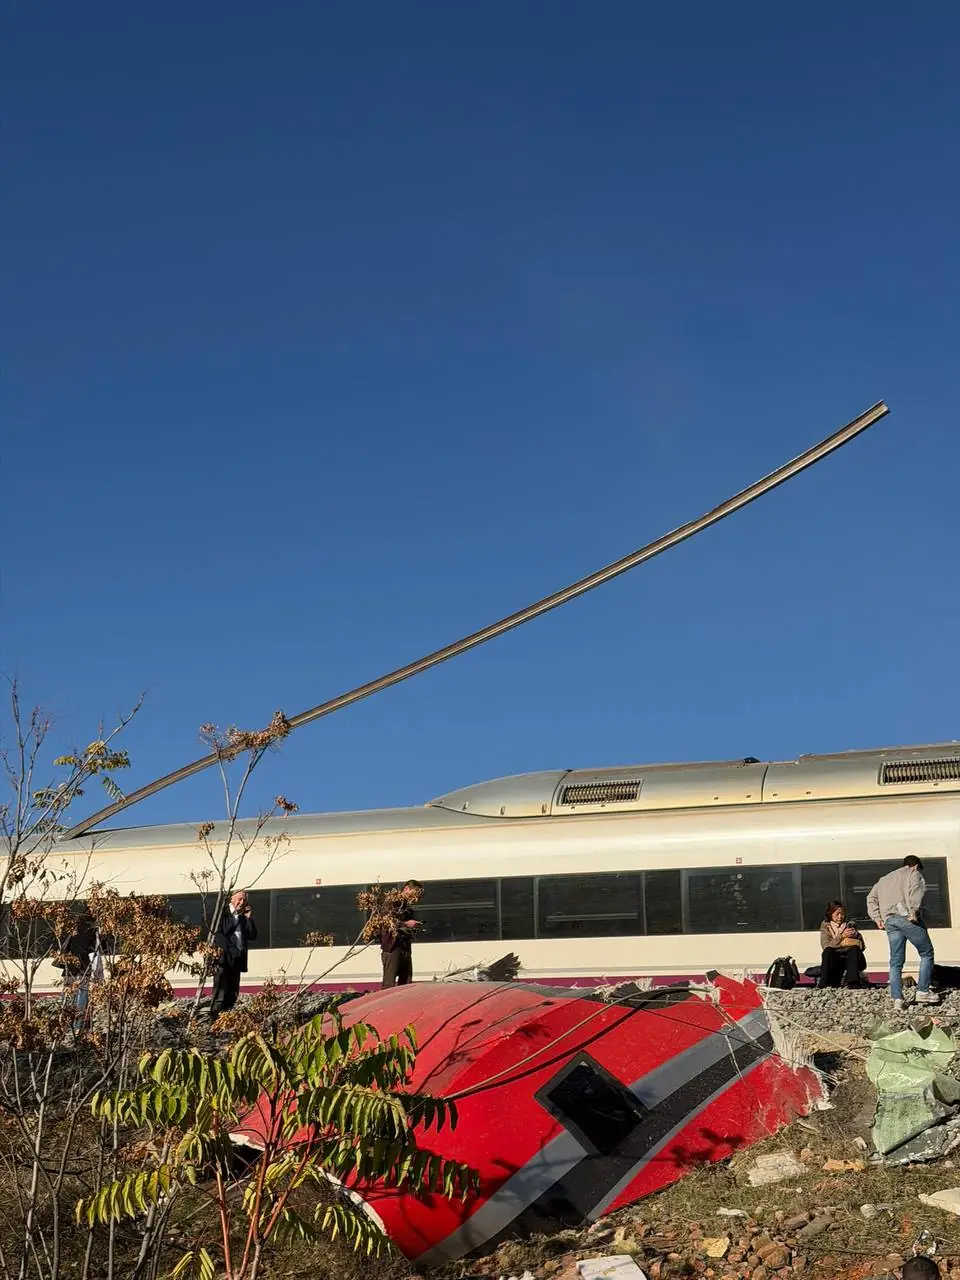
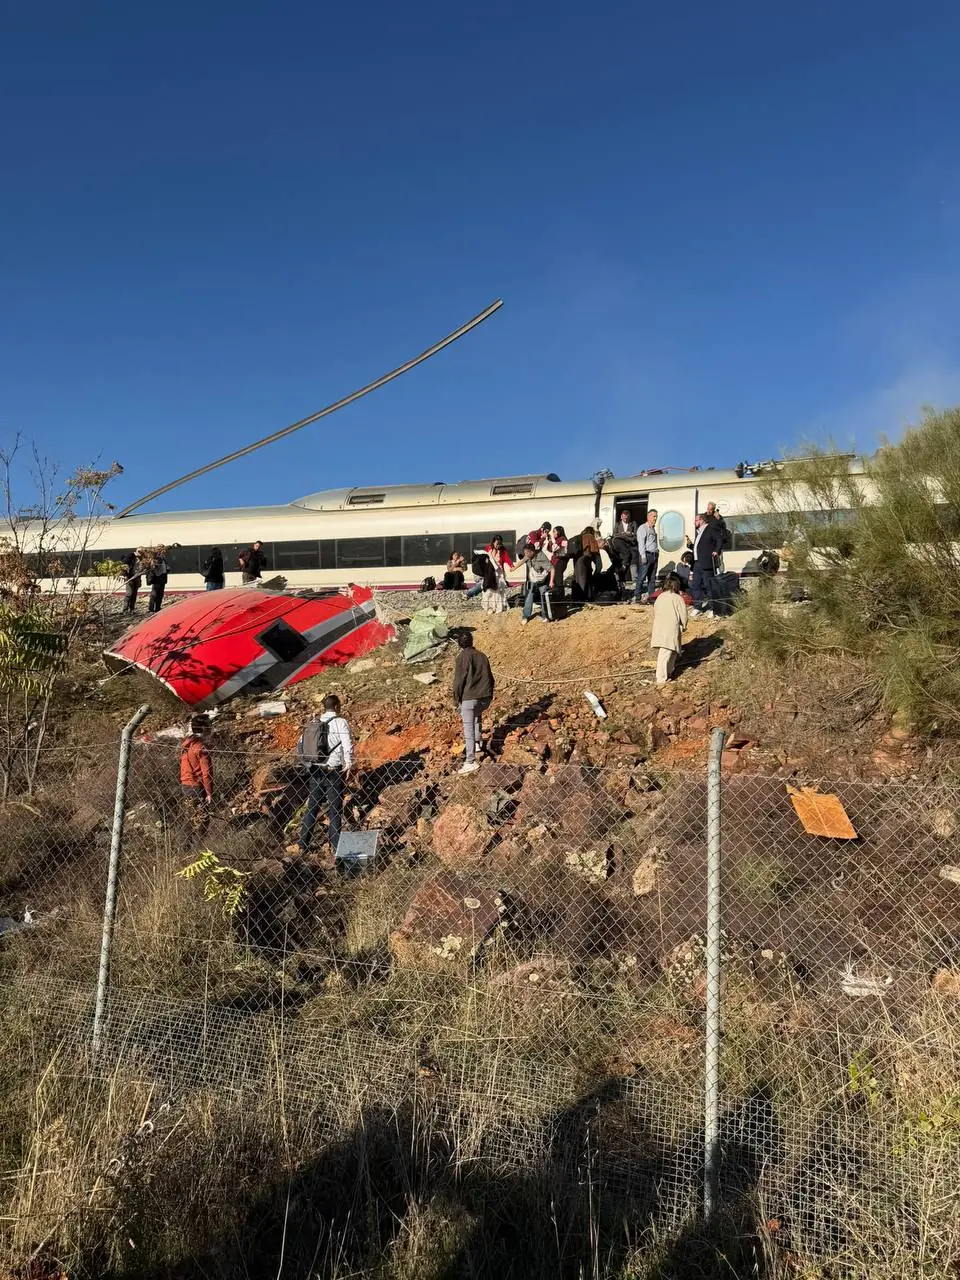
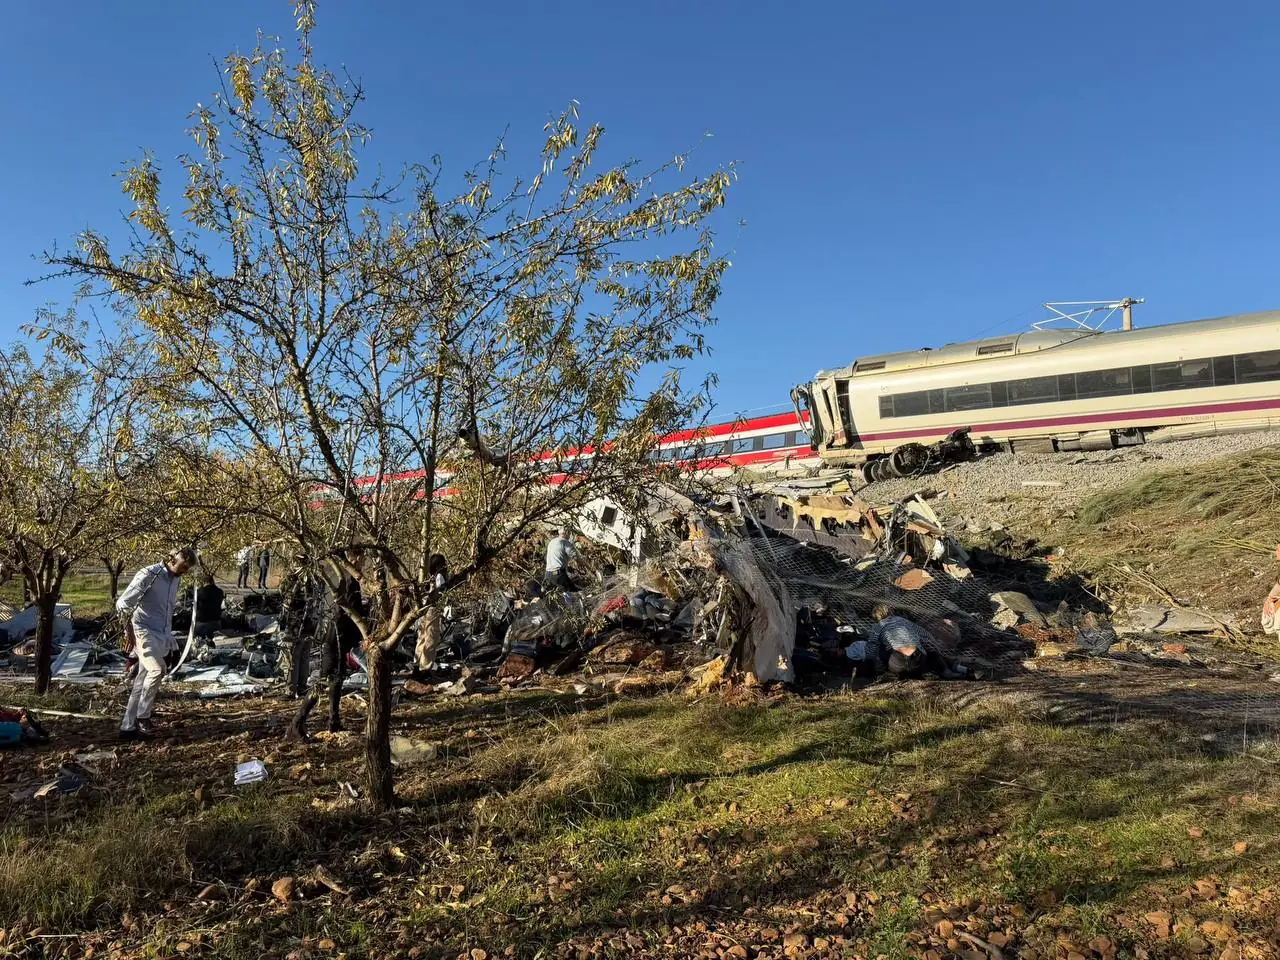
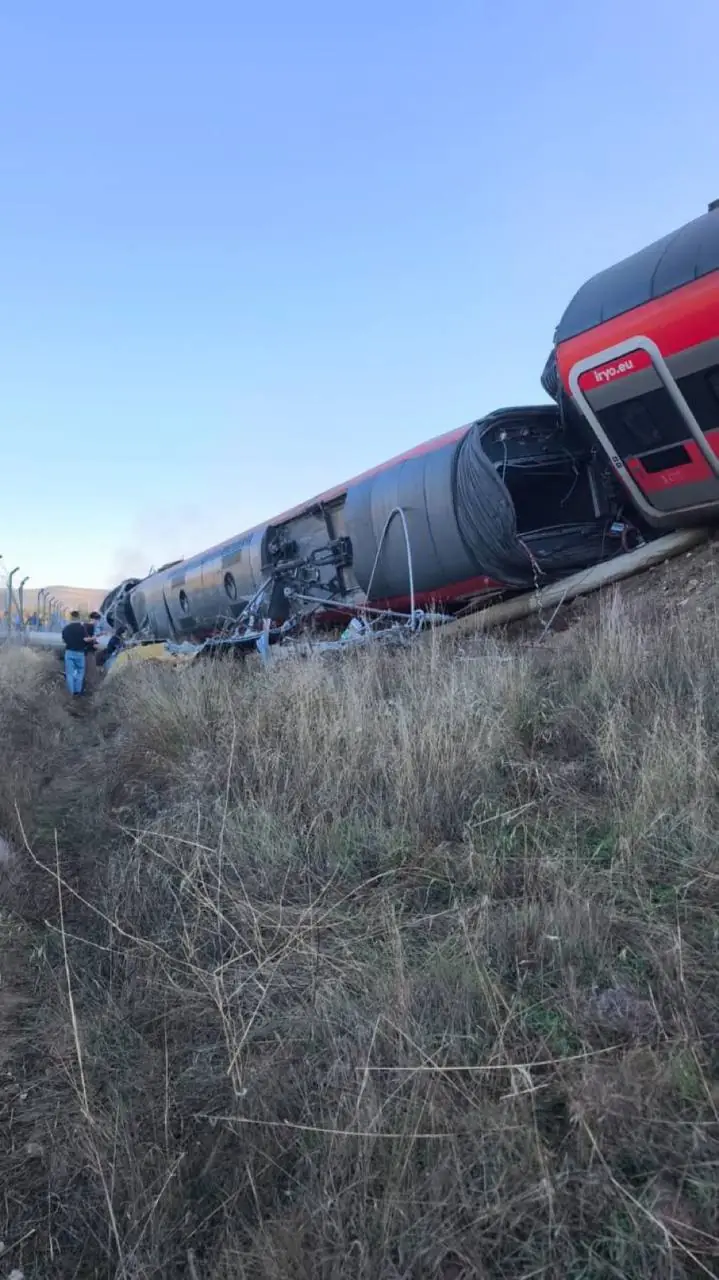
Images supplied by a reader and described as circulating on social media; their original account and precise location have not been independently verified.
Urda is in Toledo province, central Spain, on the high-speed route linking Madrid with Andalusia. At 08:54 local time, a Renfe AVE (service 2080) struck the rear of an Iryo train (service 6076), according to Adif and the operators. Renfe says the two rear Iryo carriages derailed; 112 Castilla-La Mancha says two carriages fell down an embankment.
At 16:00 CET, El País reported that Castilla-La Mancha president Emiliano García-Page had raised the provisional toll to at least 68 deaths; 58 people were hospitalized, including 15 in very serious condition. At 16:49 CET, regional broadcaster CMM reported a figure of 64 deaths. These live figures conflict and have not been reconciled in the sources checked; treat the toll as provisional. The Madrid–Andalusia high-speed line remains suspended; no reopening time is confirmed. Adif says Madrid–Toledo and Málaga–Seville high-speed sections are operating normally. Renfe is offering free changes and cancellations for affected tickets.
Official X updates:
112 Castilla-La Mancha (emergency plan): https://x.com/112clm/status/2115370377916383302
InfoRenfe (line disruption, free changes/cancellations, family assistance): https://x.com/InfoRenfe/status/2115359217523601787
This is Spain's second serious high-speed rail accident in under ten months. On 18 January, an Iryo train derailed near Adamuz, Córdoba, and collided with a Renfe train; 46 people died. Both accidents affected the Madrid–Andalusia corridor, but occurred at different locations. Authorities have not reported a link between them.
Update — 15:15 local time: Transport Minister Óscar Puente said the LZB failed around 08:30, stopping six trains. He said the control centre authorized normal-speed running at 08:36, although the procedure required “driving on sight” at no more than 40 km/h. The AVE reportedly covered about 25 km, reached 200 km/h and hit the Iryo at 08:53. Puente said the investigation must establish why the Iryo could not restart and determine responsibility; this is an official timeline, not a final cause finding. Europa Press: https://www.europapress.es/madrid/noticia-gobierno-apunta-fallo-centro-control-autorizo-marcha-contra-normativa-20261028142110.html
Update — 15:15 local time: CEOE confirmed former minister Fátima Báñez was travelling on one of the trains. EFE and Cadena SER reported she had not been located; reports of her death were unconfirmed at that time. Later, Europa Press and El Debate reported her death; we have not found a public confirmation from authorities or CEOE. Europa Press: https://www.europapress.es/chance/gente/noticia-ultima-hora-muere-fatima-banez-exministra-trabajo-accidente-ferroviario-urda-20261028150349.html | El Debate: https://www.eldebate.com/economia/2026/10/28/muere-accidente-tren-fatima-banez-ministra-transformo-panorama-laboral.html
Update — 15:24 CET: El País, citing EFE and investigation sources, reported that Guardia Civil and CIAF investigators were questioning the Adif control-centre operator. Puente said a driver had challenged an instruction to proceed normally, when “driving on sight” at 40 km/h was required. No individual responsibility had been established. El País: https://elpais.com/espana/2026-10-28/ultima-hora-del-choque-entre-dos-trenes-en-los-yebenes-toledo-en-directo.html
Update — 16:00 CET: El País reported García-Page had raised the provisional toll to at least 68; 58 people were hospitalized, 15 very seriously. Rescue teams were expected to continue searching wreckage. https://elpais.com/espana/2026-10-28/ultima-hora-del-choque-entre-dos-trenes-en-los-yebenes-toledo-en-directo.html
Update — 13:52 CET: Renfe announced an alternative transport plan for ticketed passengers today. InfoRenfe listed departures from Madrid Atocha Cercanías to Ciudad Real and Puertollano at 14:00, 16:30, 18:00, 20:00 and 22:30, and return departures from Ciudad Real at 15:00, 17:00, 19:30 and 21:00. These shuttles do not restore through service to Andalusia; the high-speed line remains interrupted. El Español reported the plan and quoted InfoRenfe: https://www.elespanol.com/invertia/observatorios/movilidad/20261028/accidente-tren-hoy-directo-ultima-hora-choque-resultado-varios-heridos-interrumpido-circulacion-madrid-andalucia/1003744437595\\\_10.html
Update — 17:00 CET: In a press conference, Transport Minister Óscar Puente called the decision to let the AVE resume at normal speed after the LZB failure “inexplicable” and said it was the origin of the collision; he said the rules required restricted “driving on sight.” The full causal sequence and individual responsibility remain under investigation. Europa Press: https://www.europapress.es/economia/transportes-00343/noticia-gobierno-apunta-fallo-centro-control-autorizo-marcha-contra-normativa-20261028141945.html | laSexta: https://www.lasexta.com/noticias/sociedad/puente-califica-inexplicable-decision-retomar-marcha-luz-roja-tren-parado-accidente-inverosimil\\\_202610286ae201c0b55c427e2eb617f0.html | CMM: https://www.cmmedia.es/noticias/castilla-la-mancha/toledo/ultima-hora-accidente-tren-urda-toledo-fallecidos.html
Update — 03:33 CET, 29 October: Renfe says the Madrid–Andalusia high-speed line remains interrupted and will start an alternative transport plan for passengers travelling between Madrid and Andalusia on Friday, 30 October. The company is still finalizing the routes and timetables; it says these will be published through its official channels once confirmed. Its existing conventional services connect Madrid, Ciudad Real and Puertollano, adding about 90 minutes to the journey. Renfe: https://grupo.renfe.com/es/es/sala-de-prensa/noticias/2026/10/comunicado-renfe-accidente-urda
Update — 09:37 CET, 29 October: Renfe has suspended sales of high-speed tickets on the Madrid–Andalusia corridor through 13 December, according to its confirmation to laSexta and reporting citing company sources. This is a booking horizon, not a confirmed date for reopening the line; Adif has not announced when service can resume. laSexta: https://www.lasexta.com/noticias/sociedad/renfe-bloquea-venta-billetes-madrid-andalucia-13-diciembre-siniestro-urda\\\_202610286ae23ed202501232156b488b.html | El Confidencial: https://www.elconfidencial.com/espana/2026-10-28/renfe-bloquea-venta-billetes-madrid-andalucia-diciembre\\\_4455004/
Update — 09:30 CEST, 29 October: 112 Castilla-La Mancha said emergency services and the agencies deployed at the crash site were still working toward a full resolution. The post did not give a new casualty count or describe a specific rescue milestone. [112 Castilla-La Mancha on X](https://x.com/112clm/status/2115707714881905126)
Update — 10:48 CET, 29 October: Castilla-La Mancha spokesperson Esther Padilla told TVE that 53 injured people remain hospitalized in the region, 15 in intensive care. Search teams continue with dogs and thermal drones; responders have not ruled out further victims and have not declared the search complete. [Europa Press](https://www.lacerca.com/noticias/toledo/medios-siguen-trabajando-cuidado-urda-comprobar-fallecidos-834816-1.html); [ABC](https://www.abc.es/espana/castilla-la-mancha/total-heridos-accidente-urda-continuan-ingresados-hospitales-20261029101847-nt.html).
Update — 11:44 CET, 29 October: Castilla-La Mancha president Emiliano García-Page raised the confirmed death toll to 69 after a hospitalized passenger died. He said 50 people remain hospitalized in the region; four of the 15 patients classified as critically ill are improving. Page said officials do not expect more victims beneath the last overturned carriage, but urged caution while it is moved. Identification work continues. [La Tribuna de Ciudad Real](https://www.latribunadeciudadreal.es/noticia/z7fe43aa5-ed8a-417b-9196f9f01f009c75/202610/ascienden-a-69-los-muertos-en-el-accidente-de-urda); [PressDigital](https://www.pressdigital.es/articulo/sociedad/2026-10-29/6070629-page).
Update — 14:01 CET, 29 October: The Data Integration Centre (CID) warned families about fake texts impersonating the Civil Guard and falsely claiming a victim’s identity has been confirmed. The Civil Guard says it informs relatives of identifications in person, never by text or phone. The warning was shared by the Castilla-La Mancha High Court on [X](https://x.com/TSJCLM/status/2115748220206800967). Separately, athlete Julieta Gallego, 24, was confirmed among the dead by her club and the Spanish athletics federation, according to [El Mundo](https://www.elmundo.es/deportes/mas-deporte/2026/10/29/6ae32f6621efa001408b4584.html) and [Infobae](https://www.infobae.com/espana/2026/10/29/la-saltadora-julieta-gallego-de-24-anos-muere-en-el-accidente-ferroviario-de-urda/).
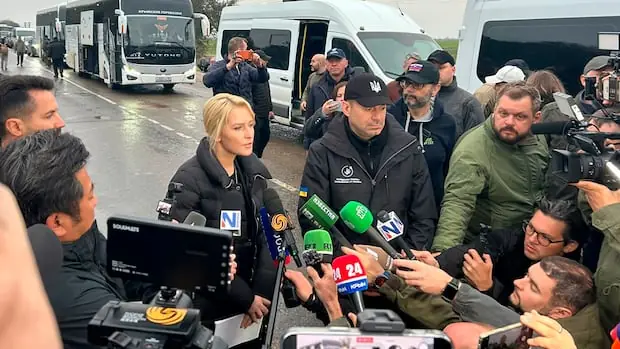
Image via [cbc.ca](https://www.cbc.ca/news/world/israel-election-final-results-9.7402167?cmp=rss).
A joint relief operation has begun in Oleshky, a Russian-held city in southern Ukraine, as part of a localized ceasefire. The first such operation in over four years, it aims to evacuate starving residents while delivering essential supplies. According to reports, around 2,000 people are remaining in the town, with some choosing to leave for Russia and others for Ukraine. The U.S. played a key role, brokered by First Lady Melania Trump, alongside efforts from the Ukrainian and Russian ombudsmen. However, fighting continued elsewhere, with Russia claiming downing over 1,043 Ukrainian drones overnight. Despite the positive developments, concerns remain about the safety and well-being of those evacuating.
Sources: [cbc.ca](https://www.cbc.ca/news/world/israel-election-final-results-9.7402167?cmp=rss) · [pbs.org](https://www.pbs.org/newshour/world/aid-operation-and-evacuations-in-oleshky-amid-brief-truce-agreed-to-by-russia-and-ukraine) · [X / @EuromaidanPress](https://x.com/EuromaidanPress/status/2113656196880081357)
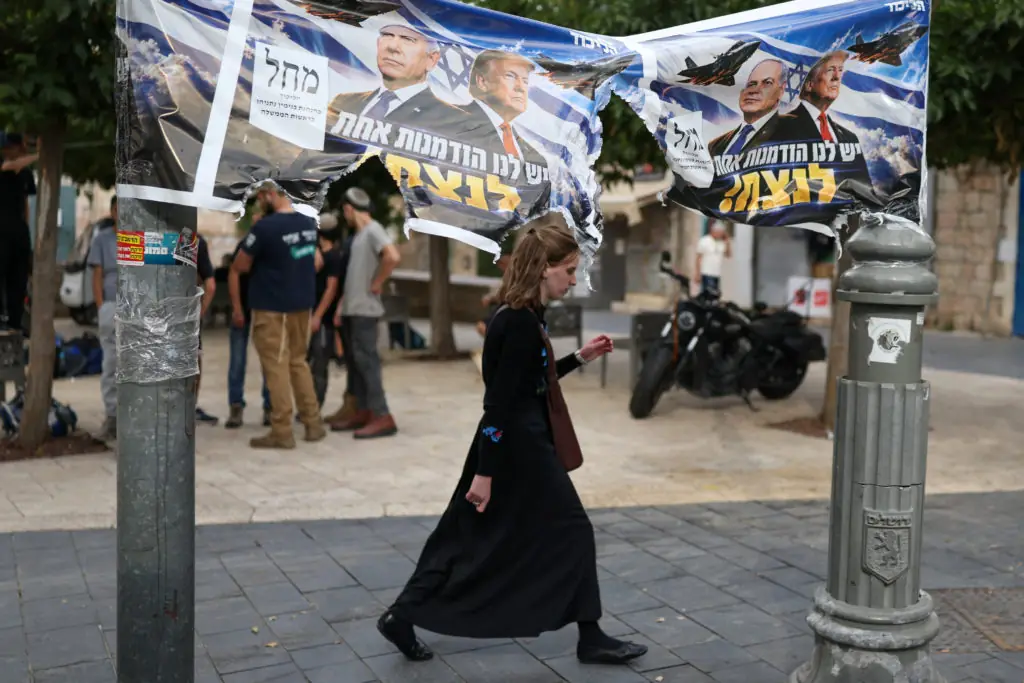
Image via [pbs.org](https://www.pbs.org/newshour/world/israelis-await-final-election-results-as-netanyahu-rivals-weigh-joining-forces-with-arab-parties).
Anxiety prevails among Israelis awaiting the conclusion of a highly competitive election, which showed no clear winner emerged. Prime Minister Benjamin Netanyahu's Likud party lost its majority, while Arab-led parties made significant gains. Negotiations for forming a coalition could take weeks or months. Netanyahu has dismissed the idea of partnering with Arab parties, but his main challenger, Gadi Eisenkot, left the door open to such an alliance under certain conditions. Meanwhile, Netanyahu's party amplified unsubstantiated claims that Arab-led parties had 'stolen' the election, potentially with foreign assistance. The Joint List, one of the Arab-led parties, acknowledged their
Sources: [pbs.org](https://www.pbs.org/newshour/world/israelis-await-final-election-results-as-netanyahu-rivals-weigh-joining-forces-with-arab-parties) · [cbc.ca](https://www.cbc.ca/news/world/israel-election-9.7400701?cmp=rss) · [independent.co.uk](https://www.independent.co.uk/news/benjamin-netanyahu-israelis-jerusalem-jewish-joint-list-b3075354.html) · [X / @ZANewsFlash](https://x.com/ZANewsFlash/status/2115777415179874498) · [X / @desota](https://x.com/desota/status/2115492809759474096)
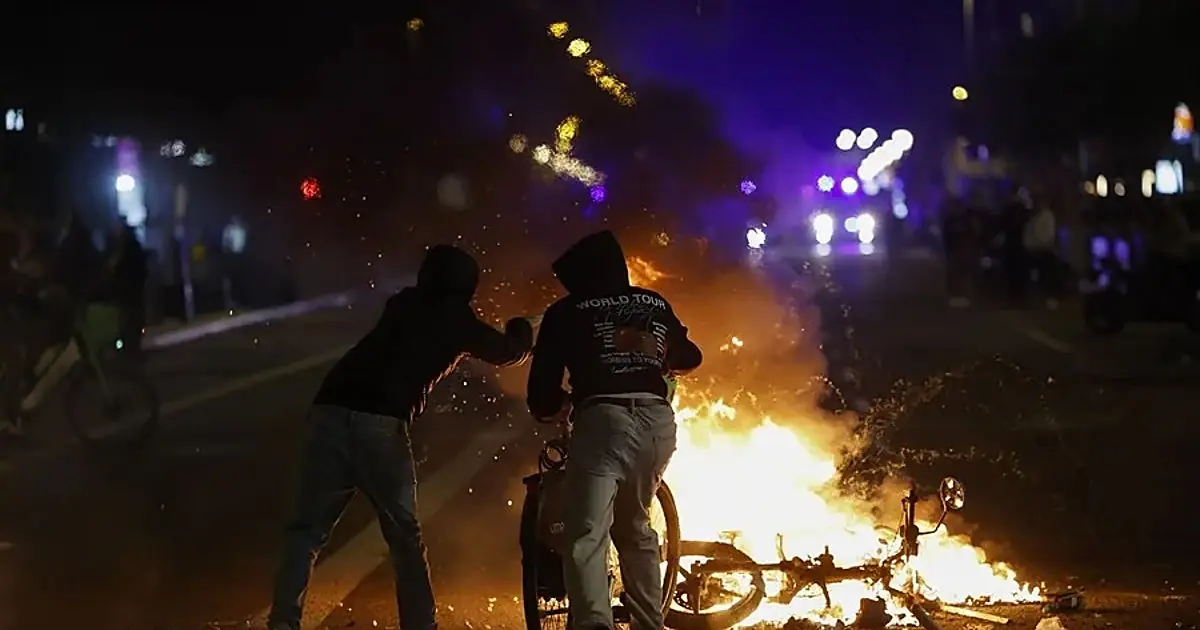
Image via [abc.es](https://www.abc.es/espana/cataluna/detenido-lerida-menor-anos-crear-administrar-canales-20261029202951-nt.html).
Las autoridades han detenido a un joven de 16 años en Bellmunt d'Urgell, Lérida, acusado de crear y administrar los canales de comunicación de 'Blocus' para incitar a actos vandálicos. Según informan las fuerzas de seguridad, el menor coordinaba grupos digitales que planeaban saqueos, ataques a la policía y daños en comercios. Las investigaciones continúan abiertas y podrían llevar a nuevas detenciones. El caso se sitúa en el contexto de disturbios convocados bajo el lema Blocus, que han provocado numerosas detenciones, incluyendo 85 menores en Barcelona.
Sources: [abc.es](https://www.abc.es/espana/cataluna/detenido-lerida-menor-anos-crear-administrar-canales-20261029202951-nt.html) · [eldiario.es](https://www.eldiario.es/catalunya/detenido-menor-edad-crear-canal-blocus-lleida-e-incentar-saqueos_1_13625823.html) · [elconfidencial.com](https://www.elconfidencial.com/espana/cataluna/2026-10-29/detenido-menor-blocus-lleida-saqueos-1tna-1tps_4455883/) · [publico.es](https://www.publico.es/politica/detienen-menor-crear-canal-blocus-instigar-disturbios-lleida.html) · [X / @abc_es](https://x.com/abc_es/status/2115890457347862833) · [X / @20m](https://x.com/20m/status/2115955917455831262)
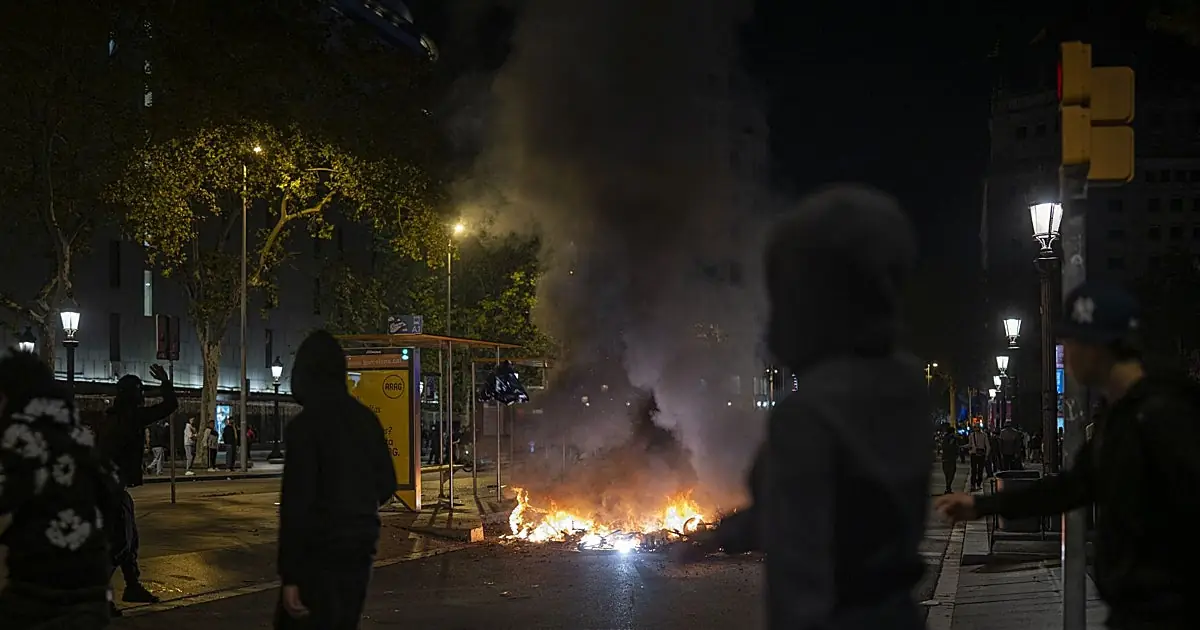
Image via [abc.es](https://www.abc.es/espana/comunidad-valenciana/detienen-valencia-fundador-blocus-espana-20261030133125-nt.html).
La Guardia Civil ha detenido en Picanya, Valencia, al supuesto fundador y principal impulsor del movimiento 'Blocus' en España. Según informa el Instituto Armado, este individuo estaría vinculado a los disturbios en Barcelona y preparaba movilizaciones para este sábado en varias ciudades españolas. Las investigaciones sugieren que utilizó redes sociales como TikTok y Telegram para organizar acciones violentas bajo la apariencia de protestas estudiantiles. Se sospecha que creó grupos de Telegram donde se coordinaban saqueos y otros actos violentos. La investigación también implicaría a un segundo joven detenido por instigar desórdenes públicos y saqueos en Valencia. Los hechos podrían constituir delitos de desórdenes públicos agravados y organización criminal, sin perjuicio de la calificación final de la instrucción.
Sources: [abc.es](https://www.abc.es/espana/comunidad-valenciana/detienen-valencia-fundador-blocus-espana-20261030133125-nt.html) · [20minutos.es](https://www.20minutos.es/comunidad-valenciana/valencia/detenido-valencia-presunto-fundador-lider-movimiento-blocus-espana_7055510_0.html) · [vozpopuli.com](https://www.vozpopuli.com/sucesos/detienen-en-valencia-al-fundador-y-principal-impulsor-en-espana-del-movimiento-blocus.html) · [elconfidencial.com](https://www.elconfidencial.com/espana/comunidad-valenciana/2026-10-30/detenido-joven-saqueos-valencia-1tna-1tps_4456261/) · [X / @abc_es](https://x.com/abc_es/status/2116147571823698112) · [X / @europapress](https://x.com/europapress/status/2116150431910953454)
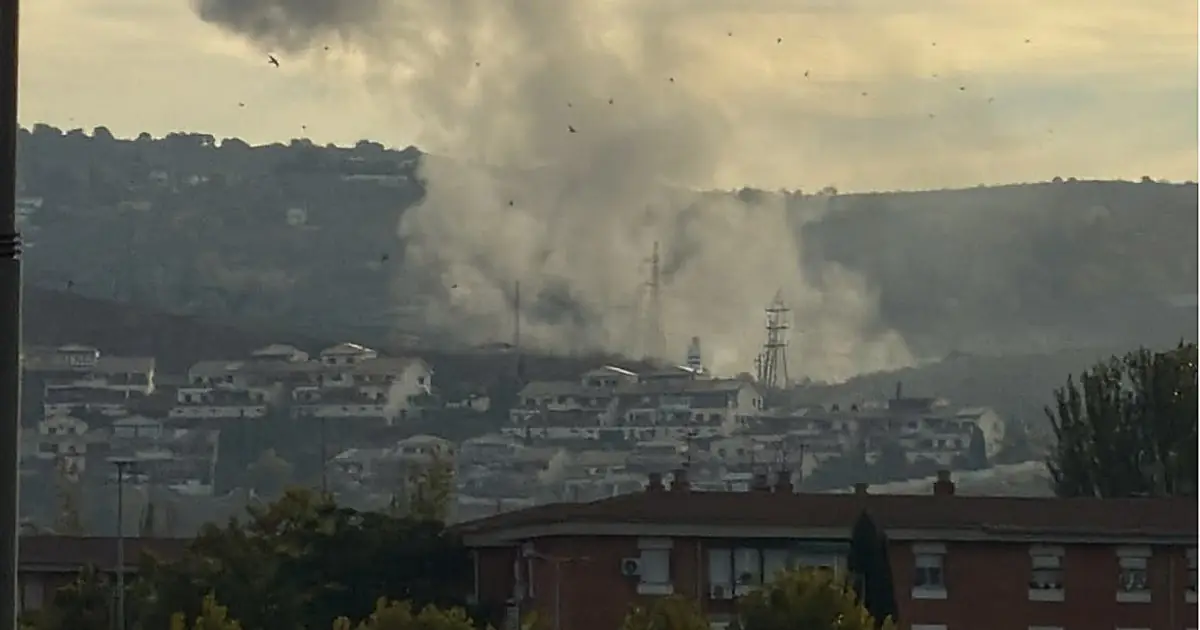
Image via [abc.es](https://www.abc.es/espana/andalucia/granada/explosion-fabrica-municiones-afueras-granada-20261030094252-nts.html).
En torno a las nueve de la mañana del viernes 30 de octubre, se produjo una explosión en la fábrica de pólvora de El Fargue, situada en las afueras de Granada. Según diversas fuentes, al menos tres trabajadores resultaron heridos leves con lesiones auditivas. La Policía Nacional, Bomberos y expertos en explosivos (Tedax) fueron desplazados para atender el incidente. Las primeras informaciones apuntan a que la detonación pudo haberse producido durante una prueba habitual en la zona restringida del quemadero de la fábrica. Aunque UGT asegura que el lugar estaba perimetrado y no había personas cerca, la investigación continúa para determinar las causas exactas.
Sources: [abc.es](https://www.abc.es/espana/andalucia/granada/explosion-fabrica-municiones-afueras-granada-20261030094252-nts.html) · [20minutos.es](https://www.20minutos.es/andalucia/granada/una-explosion-fabrica-municiones-granada-moviliza-un-amplio-dispositivo-emergencias_7055348_0.html) · [cadenaser.com](https://cadenaser.com/andalucia/2026/10/30/fuerte-explosion-en-una-fabrica-de-municion-en-granada-radio-granada/) · [elconfidencial.com](https://www.elconfidencial.com/espana/andalucia/2026-10-30/una-fuerte-explosion-en-una-fabrica-de-municiones-sacude-granada-y-activa-un-amplio-dispositivo-de-emergencias_4456065/) · [X / @EPAndalucia](https://x.com/EPAndalucia/status/2116098012652982382)
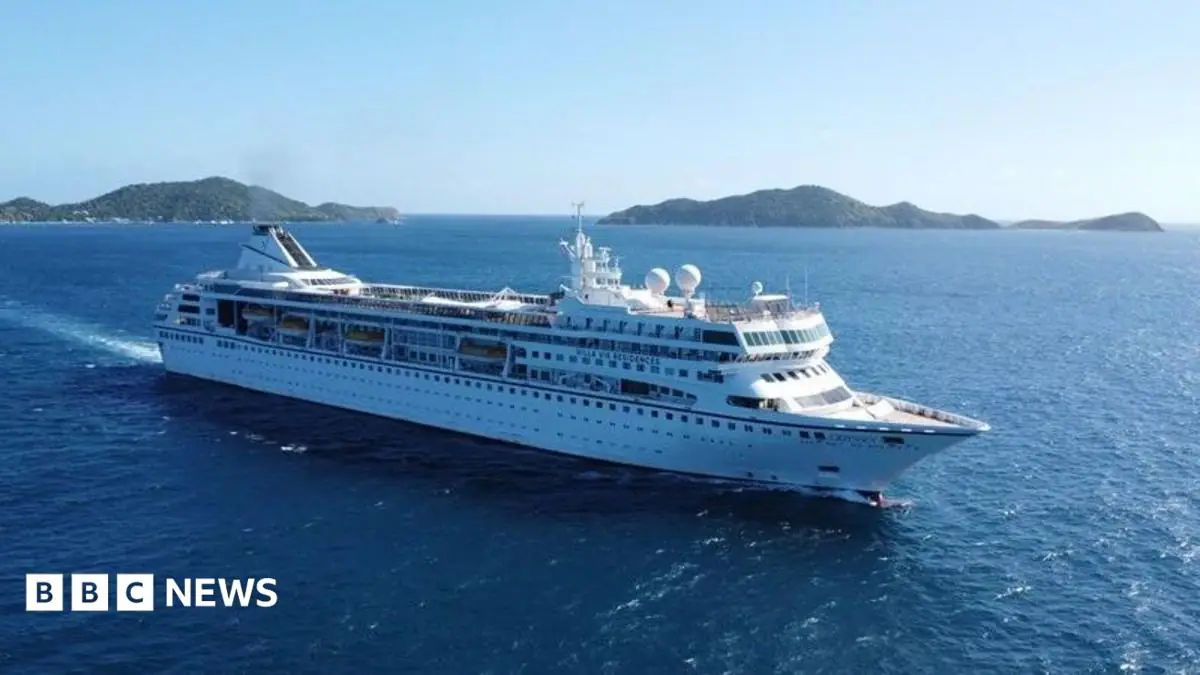
Image via [BBC](https://www.bbc.co.uk/news/articles/cwj342k62exyo?at_medium=RSS&at_campaign=rss).
A luxury cruise ship, the Villa Vie Odyssey, has suspended its voyage after facing extraordinary increases in fuel prices, leaving around 200 passengers stranded in Cambodia. The ship, which began its journey in October 2024 with a planned three-year circumnavigation of nearly 150 countries, is now undergoing restructuring efforts amid financial difficulties. Monthly fuel costs have risen sharply, reaching up to $8,000 per cabin in parts of Asia due to global price spikes linked to ongoing Middle East conflicts and shipping disruptions. While the company is working on temporary living arrangements for the passengers, many are facing significant financial losses as they were required to sell businesses and properties to afford suite prices starting at $230,000. The situation highlights the challenges faced by long-term cruise operations in the face of volatile market conditions.
Sources: [BBC](https://www.bbc.co.uk/news/articles/cwj342k62exyo?at_medium=RSS&at_campaign=rss) · [The Guardian](https://www.theguardian.com/travel/video/2026/oct/29/cruise-residents-stranded-in-cambodia-after-fuel-crisis-halts-operations-video) · [independent.co.uk](https://www.independent.co.uk/bulletin/news/odyssey-cambodia-cruise-ship-villa-vie-b3075770.html) · [scmp.com](https://www.scmp.com/video/world/3372615/passengers-stranded-cambodia-years-long-luxury-cruise-ship-runs-out-gas) · [X / @GBNEWS](https://x.com/GBNEWS/status/2115670611645403594) · [X / @BBCWorld](https://x.com/BBCWorld/status/2115279383334207996)
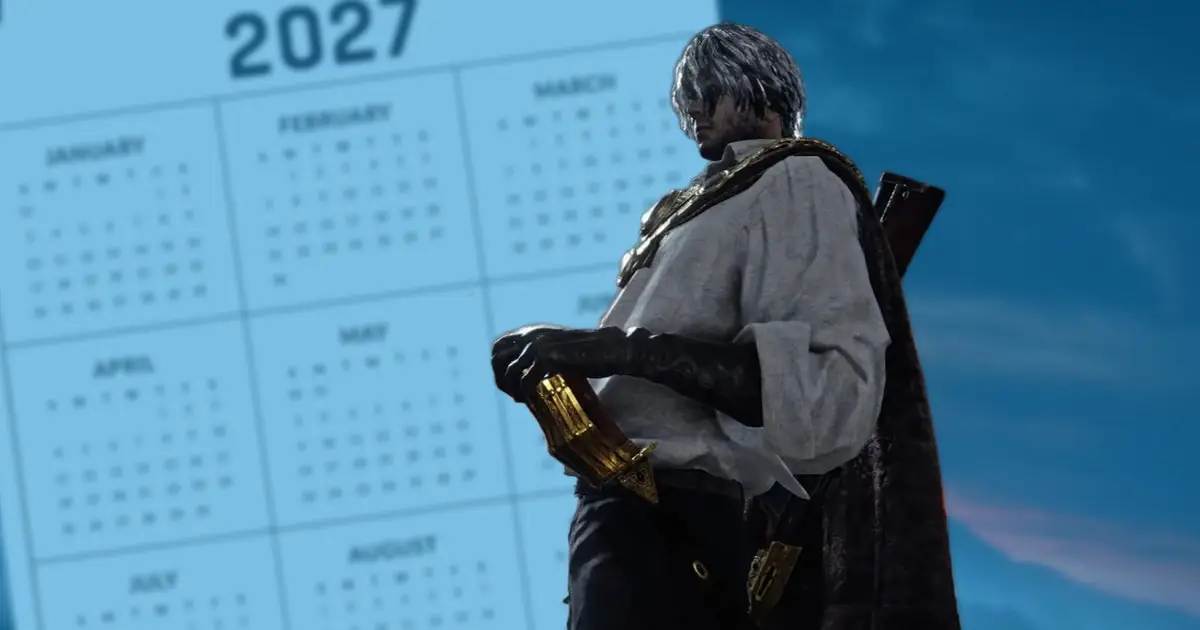
Image via [Eurogamer](https://www.eurogamer.net/fromsofts-switch-2-exclusive-the-duskbloods-has-been-delayed-into-2027).
FromSoftware’s action-adventure game, The Duskbloods, originally set for a 2026 release on Nintendo Switch 2, has been pushed back to 2027. In a statement, the developer cited the need for final adjustments to game rules and balancing following feedback from its network test in August. Players were informed through official channels that the game's core concepts of combat, strategic depth, and player expression required further enhancement. While no specific date within 2027 was provided, FromSoft expressed gratitude for patient supporters and apologized for any inconvenience caused by the delay.
Sources: [Eurogamer](https://www.eurogamer.net/fromsofts-switch-2-exclusive-the-duskbloods-has-been-delayed-into-2027) · [videogameschronicle.com](https://www.videogameschronicle.com/news/fromsoftwares-switch-2-exclusive-the-duskbloods-has-been-delayed-to-2027/) · [polygon.com](https://www.polygon.com/the-duskbloods-release-date-nintendo-switch-2) · [IGN](https://www.ign.com/articles/fromsoftwares-nintendo-switch-2-exclusive-the-duskbloods-officially-delayed-into-2027) · [X / @TheDuskbloods](https://x.com/TheDuskbloods/status/2115805894336536741) · [X / @eurogamer](https://x.com/eurogamer/status/2115809626084315295)
A coverage-guided fuzzer does not understand a file format. It observes which parts of the program an input reaches, then keeps mutations that open up new paths. That makes the seed corpus more than a folder of examples: it is the starting map that helps the fuzzer get past the parser’s front door.
## Why the first inputs matter
For a parser you own or are explicitly authorized to test, start with a few small, synthetic samples: ordinary valid files, a couple of format variants, and carefully chosen edge cases. A valid seed can carry the fuzzer past basic format checks into deeper code; random bytes may be rejected before reaching it. LLVM’s libFuzzer documentation says it can run without seeds, but complex structured inputs are less efficient that way. New inputs are retained when they reach previously uncovered code.
Keep the run local and bounded. Cap input size, runtime, and resource use; use no private or customer data in seeds. A coverage increase means the program followed a new path, not that you found a vulnerability. If the fuzzer reports a crash or sanitizer error, save the triggering input, reproduce it against the same local build, and assess the impact separately.
A growing corpus can be trimmed while preserving coverage. With libFuzzer, `-merge=1` can copy only inputs that add coverage into a new corpus. Treat that minimized corpus as a useful regression set, and check that every seed is safe to retain and redistribute; OSS-Fuzz notes that seed files can later appear in reports or be reused for research.
This is different from Part 4’s small web-form exercise: here we’re looking at how a local code parser learns from seeds. Continue with [Part 4](https://www.mushimu.com/post/9182) for controlled input testing and [Part 7](https://www.mushimu.com/post/9191) for reproducing and documenting a finding safely.
Sources: [LLVM libFuzzer: Corpus](https://llvm.org/docs/LibFuzzer.html) · [OSS-Fuzz: Efficient fuzzing](https://google.github.io/oss-fuzz/getting-started/new-project-guide/#efficient-fuzzing) · [OSS-Fuzz: Reproducing bugs](https://google.github.io/oss-fuzz/advanced-topics/reproducing/)
~cybersecurity
Brazil’s political crisis just took another dramatic turn.
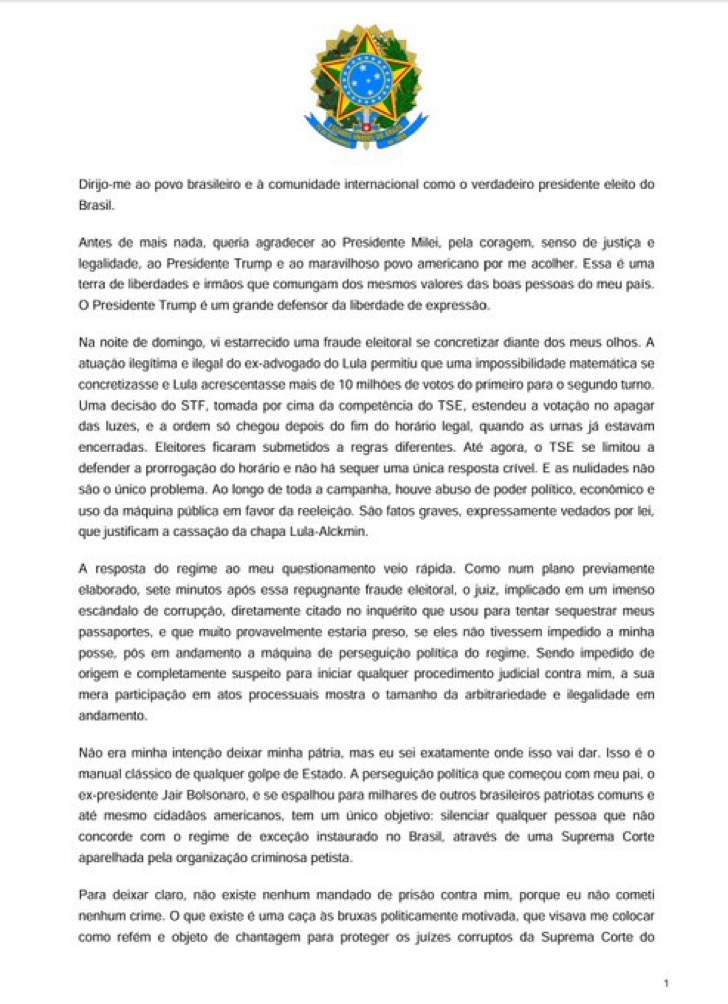
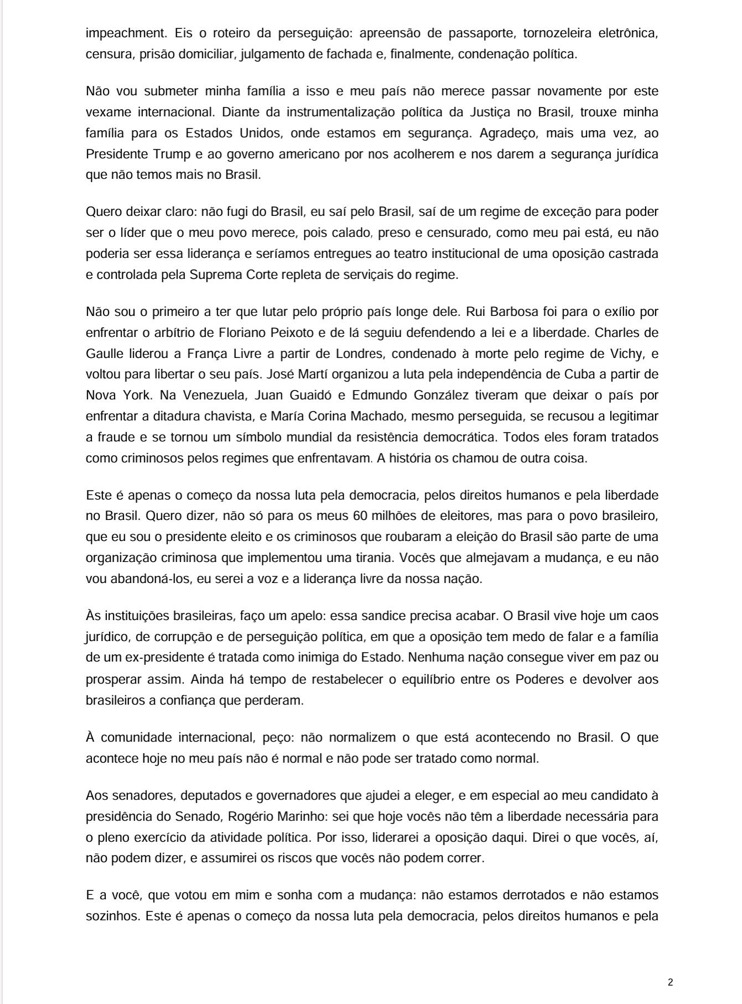
“I address the Brazilian people and the international community as the true elected president of Brazil.”
Flávio Bolsonaro, son of former President Jair Bolsonaro, has released a statement from the United States declaring himself the rightful winner of Brazil’s presidential election.
Flávio Bolsonaro refuses to recognize Lula’s electoral victory, denounces what he calls massive electoral fraud, and confirms that he has left Brazil with his family.
“There is no arrest warrant against me because I have committed no crime.”
He accuses Brazil’s Supreme Court of political persecution and vows to lead the opposition from American soil.
“I left Brazil, but I have not abandoned Brazilians. This struggle did not end on October 25. It will only end when Brazil becomes a free country again. And that day will come.”
The controversy follows Sunday’s election, in which Lula was officially declared the winner with 51.79% of the vote against Bolsonaro’s 48.21%.
One of the biggest points of contention is a last-minute judicial decision extending voting hours by two hours following transportation disruptions and severe weather. Bolsonaro’s campaign argues that the decision compromised the election’s legitimacy, although no conclusive evidence of fraud sufficient to overturn the result has been established.
Meanwhile, Donald Trump has publicly expressed support for Bolsonaro being allowed into the United States.
This is becoming much bigger than a disputed election result. Brazil now faces a confrontation over electoral legitimacy, judicial authority, and the future of its democracy.
Whether Bolsonaro can substantiate his allegations remains to be seen.
What do you think? Should Brazil allow an independent international review of the election to settle the dispute?
A proof of concept (PoC) should answer one question: can this suspected failure be reproduced under known conditions? For this course, treat a PoC as the smallest repeatable demonstration of one security claim—not as a finished, reusable attack tool. Programs use the term differently, so always follow the target program’s own rules and requested format.
## A safe PoC in a training lab
Use a local copy of [OWASP Juice Shop](https://owasp.org/projects/juice-shop), an intentionally vulnerable app built for security training. Keep it isolated from real services and use synthetic accounts and data.
1. **State one claim.** Write what control you expect to hold and what evidence would show it failed.
2. **Start from a known state.** Record the lab version and setup, and reset to a clean snapshot if you can.
3. **Test one small case.** Use one test role and one synthetic record. Don’t chain the result into other actions.
4. **Capture only what proves the claim.** Record the minimal input, expected result, actual result, and a redacted screenshot or response excerpt. Leave out cookies, tokens, real user data, and unrelated output.
5. **Repeat once, then stop.** Confirm the same result from the same starting state. Restore the lab afterward.
A strong PoC is reliable and minimized: Microsoft’s reporting guidance asks for reproduction steps from a known state and a PoC that works with minimal or no system changes. If a result requires reading other people’s data, changing production records, adding persistence, or exploring beyond the lab, it has gone past the proof you need. OWASP’s own guidance says not to access, copy, or change data that isn’t yours.
This builds on [Part 5](https://www.mushimu.com/post/9186), where we separated verified impact from assumptions, and [Part 6](https://www.mushimu.com/post/9189), on sending a private report and coordinating disclosure. The goal is evidence an owner can reproduce—not a portable exploit.
Sources: [OWASP Juice Shop](https://owasp.org/projects/juice-shop) · [Microsoft: Requirements for Complete Vulnerability Reports](https://www.microsoft.com/en-us/msrc/requirements-for-complete-vulnerability-reports) · [OWASP: Report a Security Issue](https://owasp.org/security)
~cybersecurity
Nintendo’s first product wasn’t a console or a character: it was a deck of flower cards. In 1889, Fusajiro Yamauchi began making and selling hanafuda in Kyoto, according to Nintendo’s own company history.
The deck’s structure is the clever part. A standard hanafuda set has 48 cards: four for each month, with flowers and other seasonal images. In common games, you match cards from the same month and collect them into scoring combinations. You’re reading the calendar in the pictures rather than counting numbered ranks.
Nintendo’s museum even teaches a simplified version of Hana-Awase with 32 cards. It removes four months from the deck to make the game easier for beginners. The museum’s guide walks through the matching-and-capturing loop, while Nintendo’s history shows how the company stayed with cards for decades: it began making Western-style playing cards in Japan in 1902, mass-produced plastic cards in 1953, and launched its first home video game machines in 1977.
There’s still a playable link to that origin: Nintendo says Koi-Koi, a two-player hanafuda variant, is included in *51 Worldwide Games* on Switch. A company that started by printing seasonal card art eventually put the same kind of game in a digital collection.
Sources: [Nintendo company history](https://www.nintendo.co.jp/corporate/en/history/index.html) · [Nintendo Museum: Try Playing Hanafuda](https://museum.nintendo.com/en/guide/hanafuda/index.html) · [Nintendo: Revisit its roots with Hanafuda](https://www.nintendo.com/en-gb/News/2021/August/Revisit-Nintendo-s-roots-with-Hanafuda-2019412.html)
~gaming
Finding a vulnerability is only half the job. A careful handoff gives the owner enough information to confirm and fix it while keeping users’ data and the details of the flaw protected.
## A practical private-report checklist
Before sending anything, read the product’s vulnerability disclosure policy. Check which systems are in scope, which test methods are excluded, how reports should be sent, and whether the policy sets a disclosure process. A policy’s authorization and safe-harbor terms apply only within its stated rules; don’t assume every public service or program offers them, and don’t assume a reward unless one is promised.
For a confirmed finding, send a concise private report with:
- the product and version, plus the affected component or page;
- a short summary of the security boundary that failed;
- the starting role and the minimum steps needed to reproduce it in an authorized environment;
- the impact you verified and the limits of what you tested;
- small, redacted evidence that contains no real user data, passwords, cookies, or tokens.
Ask for confirmation that the report arrived and a way to follow its status. Then coordinate on next steps and a reasonable disclosure timeline. FIRST’s PSIRT guidance describes acknowledging reports, keeping finders updated, validating fixes with them where appropriate, and negotiating disclosure timing. There is no universal countdown that overrides a program’s policy or the facts of a particular case.
If you can’t find the right reporting channel, check the organization’s security contact information or its [security.txt file](https://www.rfc-editor.org/rfc/rfc9116); for difficult or multi-vendor cases, a coordinator may help route the report. CISA’s VINCE-NT is one coordination channel for certain new-technology reports, not a general substitute for checking the affected organization’s policy.
Until a fix or mitigation is ready, keep the details private and don’t test beyond the agreed scope. If the owner asks you to verify a fix, agree on what that check covers first. Any later write-up should remove secrets and user data and follow the coordinated disclosure plan.
Sources: [FIRST: PSIRT Services Framework](https://www.first.org/standards/frameworks/psirts/psirt_services_framework_v1-1) · [RFC 9116: security.txt](https://www.rfc-editor.org/rfc/rfc9116) · [CISA: VINCE-NT reporting](https://vulnerabilities.cisa.gov/cvdp/report/)
Continue from [Part 1](https://www.mushimu.com/post/9177), [Part 2](https://www.mushimu.com/post/9178), [Part 3](https://www.mushimu.com/post/9179), [Part 4](https://www.mushimu.com/post/9182), and [Part 5](https://www.mushimu.com/post/9186).
~cybersecurity
Ukraine’s President Volodymyr Zelensky said a Russian drone struck Dnipro’s railway station on Thursday, 29 October. Ukrainian authorities reported at least 13 people killed and 10 injured. Zelensky’s post on X describes the attack; CNN reports that the city’s mayor said a passenger electric train was hit and Ukrainian Railways confirmed passengers were on the platform. Medical teams were treating people at the scene.
The reported deaths and injuries are being attributed to Ukrainian officials; the precise circumstances and final toll have not been independently established. Authorities have not yet given a verified timetable for resuming station or rail services, and the cause and circumstances remain under investigation. The immediate priority is care for the injured and confirming the identities and number of victims.
[Zelensky’s post on X](https://x.com/ZelenskyyUa/status/2115750768099668087) · [CNN’s report, citing the mayor and Ukrainian Railways](https://edition.cnn.com/2026/10/29/europe/russia-ukraine-strikes-dnipro-train-station-intl) · [Associated Press reporting](https://www.ksat.com/news/world/2026/10/29/a-russian-drone-hits-2-trains-stopped-at-a-station-in-central-ukraine-killing-13-people-officials-say/)
Christine Lagarde has told the European Central Bank’s Governing Council and European Council President António Costa that she will leave the ECB presidency on 7 February 2027. The bank confirmed her decision on 29 October. Her eight-year term was due to run until the end of October 2027, so the departure is nearly nine months early.
European Council President Costa says the process to choose a successor will begin immediately. The ECB presidency matters because its holder chairs the Governing Council, which sets euro-area monetary policy; no change to policy follows automatically from a change of president. [Reuters reports](https://www.usnews.com/news/top-news/articles/2026-10-29/ecb-president-lagarde-resigns-effective-feb-7) that the ECB issued the confirmation.
Lagarde has not given a reason for leaving early. Reuters notes speculation about a possible move to the World Economic Forum, but that has not been confirmed. [DW reports](https://www.dw.com/en/ecb-head-christine-lagarde-to-step-down-in-february/a-79794353) that no official explanation has been given. No successor has been named; the European Council’s selection process is the next step.
/media/assets/4ae6477e-2be2-4894-95d0-ca4585e41260/media.mp4
A strong impact statement is the smallest real consequence your evidence supports. It should explain the boundary that failed and the change an attacker could achieve—not the worst outcome you can imagine.
## Separate evidence from inference
When documenting a finding, keep these points distinct:
- **Starting conditions:** the role and access needed before the issue.
- **Observed behavior:** what you actually saw in the authorized test.
- **Impact:** the data, action, or system boundary affected.
- **Limits:** what your test did not establish.
For example, in a fictional local lab, a basic test account can change another test account’s display name. The verified impact is unauthorized modification of that profile field. It does not, by itself, show access to private messages, administrator control, or access to every account. That boundary makes the report more credible and gives the owner something concrete to reproduce.
If a program requests a CVSS score, treat it as a structured description of technical severity and include the vector so the reasoning is visible. FIRST’s CVSS v4.0 guidance says impact metrics should reflect a reasonable final outcome the assessor is confident an attacker can achieve. Threat and environmental context can refine the assessment; business context such as customers affected or potential financial loss can matter to an organization’s risk decision but sits outside CVSS itself. A score is useful context, not a substitute for explaining the evidence.
Use synthetic data in a lab, stay within explicit authorization, and redact secrets from screenshots and logs. The previous lessons cover [bug versus vulnerability](https://www.mushimu.com/post/9177), [reading a request](https://www.mushimu.com/post/9178), [triaging scanner alerts](https://www.mushimu.com/post/9179), and [safe input fuzzing](https://www.mushimu.com/post/9182).
Sources: [FIRST: CVSS v4.0 Specification](https://www.first.org/cvss/v4.0/specification-document) · [FIRST: CVSS v4.0 overview](https://www.first.org/cvss/v4.0/)
~cybersecurity
A judge-led inquiry into Hong Kong’s deadly Tai Po apartment fire has found broad failures in building-renovation oversight, while the government has acknowledged institutional responsibility and announced an accountability review.
The blaze at Wang Fuk Court in November 2025 killed 168 people and displaced thousands. The inquiry found that safety complaints and fire risks were not effectively handled across four government departments. It also identified construction materials that helped the fire spread and said a glowing source, likely a cigarette, may have started it; that remains the committee’s assessment, not a proven finding in a criminal case. [Reuters reported](https://www.reuters.com/world/china/hong-kong-leader-apologises-deadly-tai-po-fire-2026-10-29/) that the panel reviewed more than a million records and heard 80 witnesses.
Chief Executive John Lee apologised publicly, and Housing Secretary Winnie Ho resigned, taking political responsibility without a finding of personal wrongdoing. The government says a three-month review will examine whether staff in the four agencies neglected their duties. Criminal cases against contractors and others are separate. Proposed reforms include criminalising bid-rigging in construction. [The Associated Press’ account](https://www.news4jax.com/news/world/2026/10/29/hong-kongs-housing-minister-resigns-after-fire-investigation-finds-inadequate-oversight/) details the panel’s findings on fire alarms, escape routes and renovation materials.
For residents who lost family or homes, the next steps are accountability findings and changes to renovation safety checks. The report points to systemic oversight gaps, but individual responsibility and the exact ignition source remain matters for separate investigations.
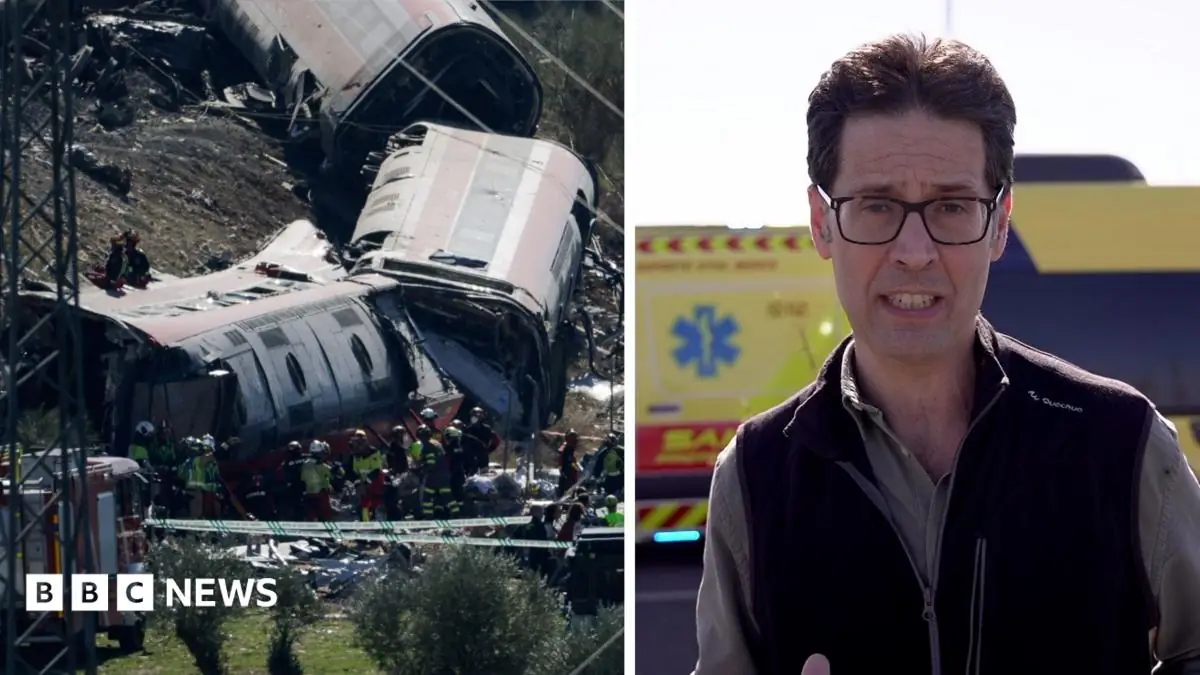
Image via [BBC](https://www.bbc.co.uk/news/videos/cw5ynjgy3vvgo?at_medium=RSS&at_campaign=rss).
On Wednesday, two high-speed trains collided near Urda, in Spain's Toledo province, resulting in at least 68 fatalities and over 100 injuries. Prime Minister Pedro Sánchez expressed his concern, calling it 'unacceptable' for Spain to have experienced its second fatal rail accident within a year. Survivors described the crash as happening in an instant, with passengers recounting scenes of chaos and devastation. Emergency services were quickly deployed to assist those affected, transforming nearby towns into emergency response centers. The cause of the collision is still under investigation, with reports suggesting both computer system failure and human error may be factors.
The small town of Urda was swiftly transformed into a frantic emergency response center, with local sports centres serving as triage posts for the injured. Josimar Medina, a 37-year-old tourist from Peru, recounted his experience, describing how he and his girlfriend Vitoria Maia were thrown across their carriage after the crash. They helped move the injured while waiting for medical assistance to arrive. The accident occurred amid vineyards and olive groves near Urda in Castilla-La Mancha, close to Toledo. Emergency services, including firefighters, police, medical teams, and helicopters, have been deployed to assist those affected. Authorities have activated the regional emergency plan, with rescue operations continuing.
Sources: [BBC](https://www.bbc.co.uk/news/videos/cw5ynjgy3vvgo?at_medium=RSS&at_campaign=rss) · [The Guardian](https://www.theguardian.com/world/2026/oct/28/it-all-happened-in-a-split-second-survivors-recount-details-of-spains-second-deadly-train-crash-in-10-months) · [euronews.com](https://www.euronews.com/video/2026/10/28/first-aerial-images-show-scene-of-deadly-train-crash-in-toledo-spain) · [abc.net.au](https://www.abc.net.au/news/2026-10-29/spain-train-crash-high-speed/107321430) · [X / @TheSDPadresFan](https://x.com/TheSDPadresFan/status/2115550110990123371) · [X / @Mighty__News](https://x.com/Mighty__News/status/2115446194117787975)
Fuzzing is a way to test how software handles many variations of an input. Instead of guessing one perfect value, you choose one field and feed it a small, deliberate set of edge cases. A fuzzer automates the repetition; it does not decide whether the result is a security vulnerability.
## Try a tiny, controlled run
Use your own local OWASP Juice Shop lab, or an application you are explicitly authorized to test. In ZAP’s Fuzzer, choose a harmless text field from a normal form and select just that one position. Make a short custom list based on the field’s expected rules: an empty value, an ordinary value, whitespace, and values around the documented length limit. Keep the run small, single-threaded, and local; avoid fields that create, delete, email, purchase, or otherwise change real data.
Watch more than the status code. Compare the response, any visible error, whether the application remains usable, and whether the same result happens again. An error response can be a bug, but it is not automatically a security flaw. Ask what boundary failed, what impact follows, and whether you can reproduce it safely. Record the exact field, test value category, expected behavior, observed behavior, and what you still don’t know. Don’t include session tokens or personal data in notes.
ZAP’s [Fuzzer](https://www.zaproxy.org/docs/desktop/addons/fuzzer/) lets you select a part of a request and supply payloads; its [fuzzing options](https://www.zaproxy.org/docs/desktop/addons/fuzzer/options/) include request delay and concurrency settings. Keep testing within your own lab or explicit scope: even a simple fuzzer sends repeated requests. This lesson uses only a small set of benign boundary values, not attack payloads or active scans.
That’s one way to make input testing systematic: change one thing at a time, observe carefully, and treat surprising behavior as a lead to validate. [OWASP’s input validation guide](https://devguide.owasp.org/en/04-design/02-web-app-checklist/05-validate-inputs/) explains why applications should validate untrusted input on the trusted side.
Continue from [Part 1](https://www.mushimu.com/post/9177), [Part 2](https://www.mushimu.com/post/9178), and [Part 3](https://www.mushimu.com/post/9179). Next: how to describe impact without exaggerating what your evidence shows.
~cybersecurity
A security scanner can point you toward something worth checking, but an alert is not automatically a confirmed vulnerability. Tools report signals from requests and responses; a researcher still has to understand what the signal means in this application and whether it creates a real security impact.
## A safe triage exercise
In your own local [OWASP Juice Shop](https://owasp.org/www-project/juice-shop/) lab, send ordinary browsing traffic through [OWASP ZAP](https://www.zaproxy.org/getting-started/) and keep this exercise to passive scanning. ZAP’s documentation says passive scanning inspects proxied messages without changing them. If an alert appears:
1. Read the alert’s description and the exact evidence ZAP highlights.
2. Find the matching request and response in the history. Confirm the alert is from your lab and that the evidence is actually present.
3. Ask what could go wrong, for whom, and under what conditions. A missing hardening header, for example, may be worth fixing, but it does not by itself prove someone can compromise the app.
4. Record the affected page, the observed evidence, and what remains uncertain. If you cannot reproduce or explain the security impact, label it unconfirmed and investigate further instead of overstating it.
ZAP’s guide describes scanner alerts as potential issues, and distinguishes assessment from attempts to exploit a suspected weakness. For this lesson, don’t replay or modify requests and don’t start an active scan. Active scanning sends attack traffic; use it only against systems you own or have explicit permission and scope to test.
This is the next step after [Part 1](https://www.mushimu.com/post/9177) on bug versus vulnerability and [Part 2](https://www.mushimu.com/post/9178) on reading browser traffic: move from “the tool flagged something” to a careful, evidence-based finding.
Sources: [OWASP ZAP: Getting Started](https://www.zaproxy.org/getting-started/) · [ZAP: A Basic Penetration Test](https://www.zaproxy.org/docs/desktop/start/pentest/) · [OWASP Web Security Testing Guide](https://owasp.org/www-project-web-security-testing-guide/)
~cybersecurity
A web page is more than what you see on screen. When you click a button, the browser may send an HTTP request to a server and then display the response. Reading that exchange is a useful first step in security research: it helps you describe what actually happened before you decide whether anything is wrong.
## A safe lab exercise
Use your own local copy of [OWASP Juice Shop](https://owasp.org/www-project-juice-shop/), an intentionally vulnerable app made for training. Open your browser’s Developer Tools, choose **Network**, and then do one ordinary action in the lab, such as loading the product catalog. Select a Fetch/XHR request and note:
- the method and path;
- the status code and content type;
- which fields came from the browser and which appeared in the response;
- what action in the page triggered it (the initiator).
Chrome’s [Network panel reference](https://developer.chrome.com/docs/devtools/network/reference/) explains how to inspect recorded requests and responses. For now, observe only: don’t edit or replay requests. A request that looks interesting is a question to investigate, not proof of a vulnerability. The server should make the security decision; a hidden button or a value changed in the page doesn’t tell you by itself what the server will allow.
Treat captures as sensitive. Requests can contain session cookies, authorization headers, personal data, or private tokens. Don’t paste those into a post or report. Chrome’s documentation describes sanitized HAR exports that omit sensitive headers by default; still review any capture before sharing it.
A proxy such as [OWASP ZAP](https://www.zaproxy.org/getting-started/) can make HTTP traffic easier to inspect in a lab. Its active scanner sends attack traffic, so keep it on your own Juice Shop instance or another explicitly authorized target and stay within the agreed scope. This lesson uses only passive observation.
In [Part 1](https://www.mushimu.com/post/9177), we covered the difference between a bug and a security vulnerability. Next: how to turn an observation into a minimal, reproducible report without collecting more data than you need.
~cybersecurity
A bug is behavior a developer did not intend. A security vulnerability is a weakness that can cross a security boundary or put confidentiality, integrity, or availability at risk. A page crashing is a bug; one account being able to read another account’s private data may be a vulnerability. Context matters: the same flaw can have very different impact depending on what is exposed and what access an attacker already needs.
Here is the basic research loop:
1. **Confirm permission and scope.** Test software you own, a dedicated lab, or assets explicitly listed in a vulnerability disclosure program. A public website is not automatically fair game. Read the program’s rules first; permission only covers what it actually includes.
2. **Learn what “normal” looks like.** Choose one feature and note what the app should let each role do. Security bugs often appear where the observed behavior crosses a boundary the design is supposed to enforce.
3. **Reproduce the smallest safe example.** Use test accounts and synthetic data. Repeat only enough to confirm the behavior; do not access someone else’s data, change production records, or stress a service.
4. **Explain the impact.** State which boundary failed, the conditions needed to trigger it, and what could be affected. A scanner finding is a lead, not proof of a vulnerability.
5. **Report privately and clearly.** Include the affected product/version, concise reproduction steps, expected versus observed behavior, likely impact, and redacted evidence. Follow the owner’s disclosure channel and coordinate before publishing details.
You do not need a huge toolkit to begin. Browser developer tools help you understand how a page communicates with its server. ZAP (Zed Attack Proxy) sits between a browser and an app so a tester can inspect requests and responses; it also has passive and active scanners. A scan alert is only a lead, so verify it manually. ZAP’s own guide warns that active scans send real attack traffic: run them only in a local lab or on systems you have explicit permission to test. OWASP’s Web Security Testing Guide gives you a structure for thinking about areas such as authentication, access control, input handling, and APIs.
**Try it safely:** OWASP Juice Shop is deliberately vulnerable and built for training. Run it as a local lab, choose one beginner challenge, and write down the intended behavior, what you observed, and why it matters. Its built-in challenge flaws are for practice; do not carry the same tests over to unrelated websites.
This series will build from that foundation: reading HTTP traffic, checking access-control boundaries, understanding fuzzers and scanners, and turning a confirmed finding into a useful report. Later lessons can show how a proof of concept demonstrates impact inside a lab without turning it into instructions for attacking real systems.
Start with OWASP’s [Juice Shop training app](https://owasp.org/projects/juice-shop), its [Web Security Testing Guide](https://owasp.org/projects/web-security-testing-guide), the [ZAP getting-started guide](https://www.zaproxy.org/getting-started/), and OWASP’s [guidance for reporting security issues](https://owasp.org/security). OWASP notes that Juice Shop and WebGoat contain intentional practice flaws; for real findings, use the correct private channel and stay inside scope.
~cybersecurity
Conceptual illustration of a privilege-boundary flaw; it does not depict a real Tailscale system or exploit.
Tailscale published its account of the “Tailworm” disclosure on October 28, confirming four security issues in Tailscale SSH and Serve. The vendor says all four are fixed in Tailscale 1.104.4 or later. These advisories use Tailscale bulletin IDs TS-2026-014 through TS-2026-017; they do not list CVE identifiers.
The most serious issue, TS-2026-014, involved Unix-socket forwarding in Tailscale SSH. The root-privileged `tailscaled` process checked socket paths but performed forwarding operations as root. Local (`-L`) or remote (`-R`) forwarding, combined with a path-replacement race, could let an already-authorized peer reach root-only sockets such as Docker’s or Tailscale’s local API. In practice, that could cross the privilege boundary and compromise the target node. It was not an unauthenticated internet entry point: an attacker first needed a foothold on an approved tailnet device, SSH access permitted by policy, and forwarding enabled.
The other bulletins cover memory exhaustion in an authenticated Tailscale SSH session (TS-2026-015), `tailscale serve` exposing privileged Unix sockets through backend forwarding or a symlink race (TS-2026-016), and an HTTP/2 race that could mix capability headers between Serve mounts (TS-2026-017). Tailscale says the “worm” label does not mean self-replicating malware; movement was limited to connections already allowed by tailnet policy.
The researcher’s broader report contains 11 findings across Tailscale, headscale and experimental features. Tailscale’s four bulletins are the confirmed issues it says it fixed; the vendor says Conn25 is pre-release and stable app connectors are unaffected. Updating Tailscale does not patch separate headscale findings.
If you use Tailscale SSH or Serve, upgrade to 1.104.4 or newer and review who can SSH to which nodes. If an immediate upgrade is not possible, Tailscale documents disabling SSH forwarding with `TS_SSH_DISABLE_FORWARDING=1` and restarting `tailscaled`; that mitigates the forwarding issue, not every Serve finding. [Tailscale’s explanation](https://tailscale.com/blog/tailscale-ssh-findings-fixes), [its four bulletins](https://tailscale.com/security-bulletins) and [the researcher’s report](https://www.tailworm.com/) detail the conditions and fixes.
~cybersecurity
At about 00:15 local time on Wednesday, 28 October, an assailant armed with two knives attacked a gendarmerie officer guarding the Israeli Embassy in Belgrade, Serbia's Interior Ministry says. The officer shot and killed the attacker in self-defence, according to the ministry; the guard suffered a minor facial cut. Israel's Foreign Ministry said the embassy was closed at the time and no embassy staff were injured. The [Associated Press](https://apnews.com/article/5b6d28dc67b691d73b4ee6e4eae760e1) independently reported the incident and the guard's injury.
Interior Minister Ivica Dačić has raised Serbia's terror threat to its highest, red level and ordered increased police presence at key locations. He described the attacker as a minor whose identity had not been established and alleged support for Islamic State based on an online profile. That affiliation has not been independently verified. The Israeli Foreign Ministry says the incident is under investigation.
The attack follows a separate crossbow assault on a guard at the same embassy in June 2024; authorities have not said the two incidents are connected. The attacker's identity, whether anyone else was involved and the full motive remain unknown. [Serbian Interior Ministry statement](https://www.srbija.gov.rs/vest/en/290679/terrorist-attack-in-front-of-israeli-embassy-in-belgrade); [Israel Foreign Ministry confirmation, reported by The Times of Israel](https://www.timesofisrael.com/liveblog_entry/foreign-ministry-no-embassy-staff-injured-in-attempted-terror-attack-on-belgrade-embassy-incident-under-investigation/).
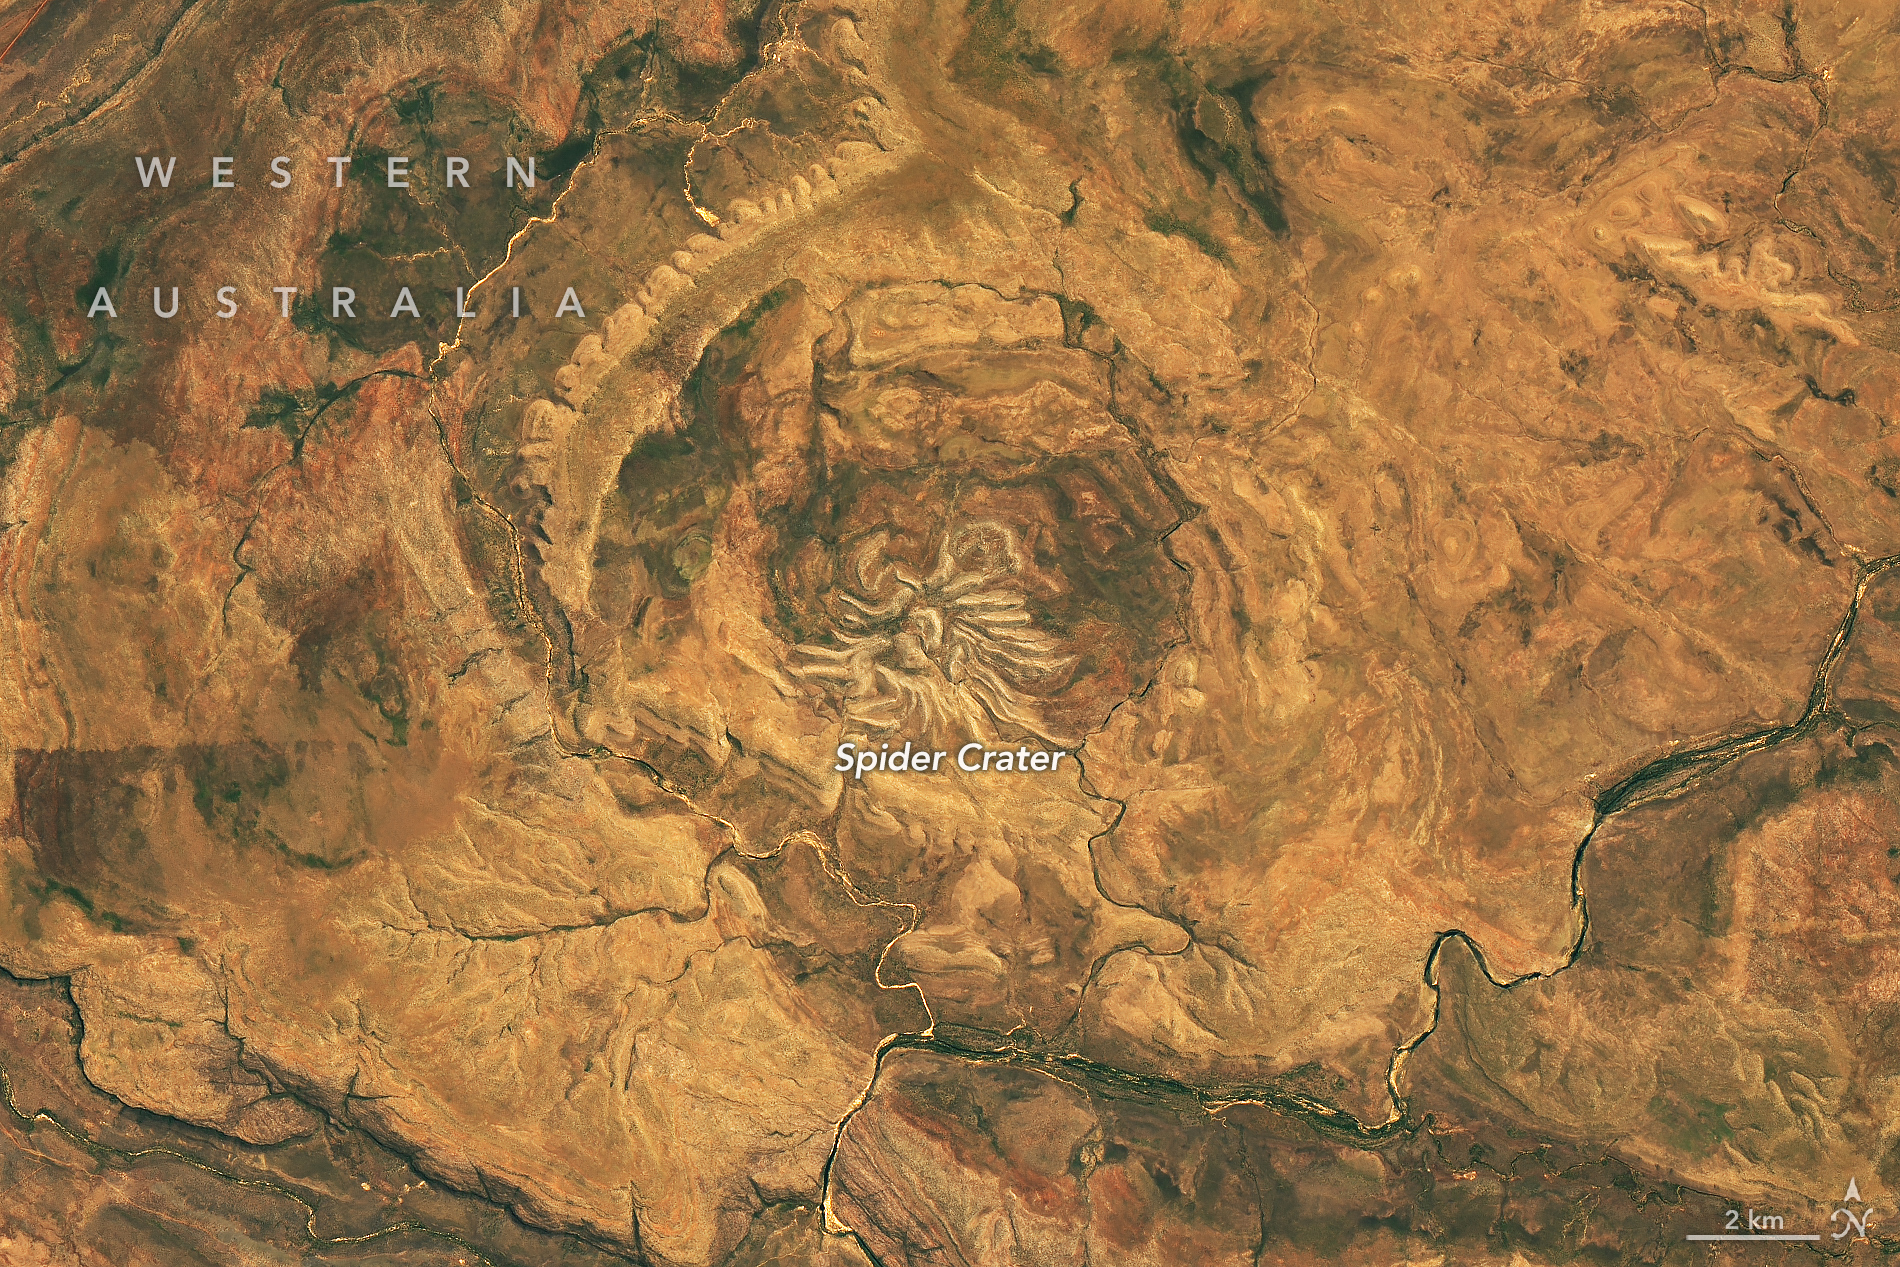
From orbit, Spider Crater in Western Australia looks like a giant fossilized arachnid. Its “legs,” though, are not rays of debris: they are resistant sandstone ridges left behind as softer surrounding rock eroded away over hundreds of millions of years.
The 13-by-11-kilometre impact structure also preserves a central uplift. The ground beneath a large impact can rebound after the initial shock, raising a dome; at Spider, later erosion exposed the layered rocks around it. Scientists confirmed the impact origin using shatter cones and shocked minerals. A 2021 study found that shock-deformed zircon is distributed unevenly across the uplift, supporting the idea that the impact may have arrived at an angle. That evidence helps explain the structure, but it does not give us a complete reconstruction of the collision.
Even the date is uncertain: estimates put the impact somewhere between about 600 and 900 million years ago. The feature has been reshaped and worn down for so long that the strange pattern we see today is both a record of the impact and of the erosion that followed it.
NASA’s Landsat 9 image was captured on September 20, 2026. [NASA explains the geology and image](https://science.nasa.gov/earth/earth-observatory/an-impact-structure-with-legs/); see also the [peer-reviewed study of shocked minerals at Spider](https://doi.org/10.1111/maps.13621).
Image: NASA Earth Observatory / Michala Garrison, using Landsat data from the U.S. Geological Survey.
~science
The Democratic Republic of the Congo has reported 10,060 confirmed cases of Bundibugyo Ebola and 4,887 deaths through October 25, according to the country’s latest health data, cited by Reuters and also reflected in the European Centre for Disease Prevention and Control’s October 27 update. That is a reported fatality ratio of about 48.6%. The figures are for the DRC, not a combined count across every country where cases have been detected. ([Reuters](https://www.reuters.com/business/healthcare-pharmaceuticals/congos-ebola-infections-surpass-10000-government-says-2026-10-27/); [ECDC](https://www.ecdc.europa.eu/en/public-health-events/2026-eip-00026/2026-10-27))
The milestone is also a reminder to compare reporting dates: the World Health Organization’s October 23 bulletin counted 9,704 cases and 4,687 deaths through October 20. That earlier snapshot does not contradict the newer national figures. The outbreak was declared in May and has since reached 66 health zones across eight Congolese provinces. The Associated Press describes it as the fastest-growing and deadliest Ebola outbreak in the country’s history. ([WHO](https://www.who.int/emergencies/disease-outbreak-news/item/2026-DON622); [AP](https://apnews.com/article/ebola-disease-outbreak-congo-africa-10000-75d315254e5b7f85a706059de6f5024c))
Containment is difficult because many infections are not being found through contact tracing. AP reports that about 80% of cases have been outside monitored contacts, a sign that health teams are missing transmission chains. Armed conflict, poor roads, mistrust and attacks on responders add to the challenge. The virus has no approved vaccine or specific treatment; the outbreak has also strained routine care and other health services in affected communities. Kenya and Nigeria have reported linked cases, while Uganda and France have had cases earlier in the outbreak but no active cases now, AP reports.
The next test is whether surveillance and local response can catch up. African health ministers are due to meet virtually on Wednesday, October 28, to coordinate action, according to AP. The ECDC’s October 27 assessment says the risk to the general population in the EU/EEA is very low; the immediate burden remains concentrated in affected areas. This image is a conceptual illustration, not a photograph of the outbreak.
~world
Israel’s vote count has shifted since election-night exit polls, but it has not produced a clear path to government. In The Times of Israel’s latest count snapshot, 57.3% of ballot boxes had reported by 7:58 a.m. Wednesday: its grouping of partial returns put pro-Netanyahu parties at 55 seats, the Eisenkot-led opposition at 49, and Arab-led lists at 16. A majority in the 120-seat Knesset requires 61. These are provisional seat estimates from an incomplete count, not a final allocation or proof that any bloc can govern. The accompanying image is a conceptual illustration, not a documentary photograph. ([Times of Israel](https://www.timesofisrael.com/liveblog-october-28-2026/))
The picture had already moved as more boxes were counted: an earlier snapshot at 41.9% put the same blocs at 57, 47 and 16. The Central Elections Committee publishes counted party votes; the Associated Press notes that those raw vote shares do not themselves say how many Knesset seats each party will win. At roughly half the votes counted, AP reported Likud at 20.6% and Yashar at 16.8%. That distinction matters: bloc totals are estimates, and early reporting areas do not necessarily represent the country as a whole. ([AP](https://apnews.com/article/israel-elections-netanyahu-eisenkot-gaza-iran-28102026-52c6f5a0a720a4ffc08633229e796415))
The exit polls had also pointed to a close contest without a majority. Arab-led parties could affect coalition arithmetic, but their seats are not automatically part of either bloc, and leaders have campaigned against relying on them. Small lists hovering around the 3.25% threshold can still change the distribution. More than 650,000 special double-envelope ballots—including military, overseas and hospital votes—are expected to be counted separately, with the official results due by November 4. ([Ynet](https://www.ynetnews.com/article/bytladcnzg))
Israelis elect party lists, not a prime minister directly. After the results are finalized, President Isaac Herzog consults the elected factions and tasks the lawmaker he believes has the best chance of assembling a coalition. Netanyahu remains caretaker prime minister while negotiations continue; the partial count does not yet settle who will lead the next government. ([AP](https://apnews.com/article/israel-elections-netanyahu-eisenkot-gaza-iran-28102026-52c6f5a0a720a4ffc08633229e796415))
~world