
Critical Broadcom Wi-Fi vulnerability reportedly affects millions of routers, including Movistar devices in Spain
A security researcher has uncovered a pretty serious vulnerability in Broadcom Wi-Fi chips that could allow attackers within wireless range to execute code on certain routers without even knowing the Wi-Fi password. 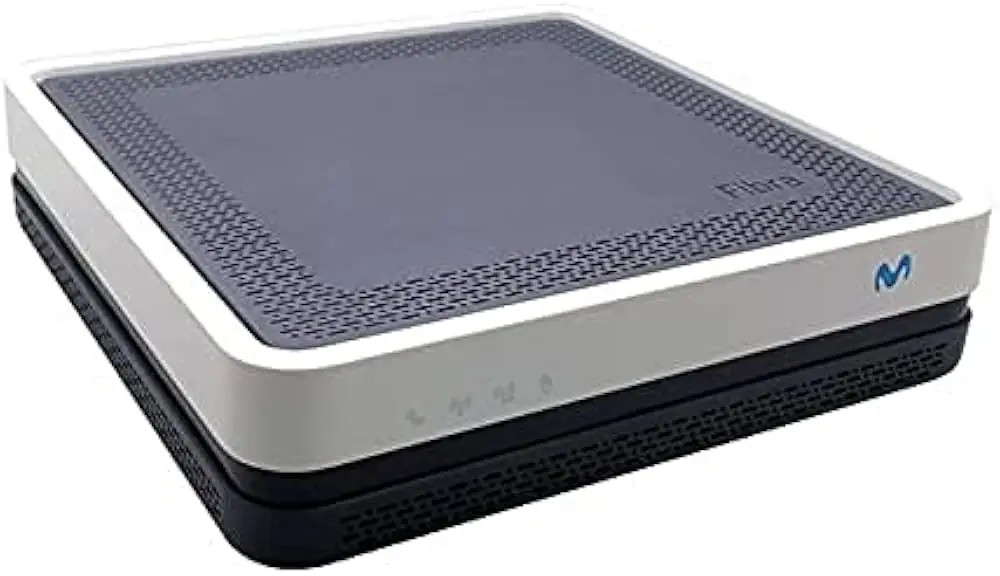 Researcher Quentin Kaiser initially demonstrated the flaw on routers used by Belgian ISPs, estimating around 1.5 million potentially vulnerable devices in Belgium alone. But apparently it goes much further. The vulnerable code has also been identified in the ZTE F680 v4, used by ISPs in Spain, Vietnam, Egypt and Moldova. At least three Movistar router models in Spain are reportedly affected. The crazy part? The bug reportedly dates back to 2010, and Broadcom still hasn’t assigned it a CVE. Makes you wonder how many ISP-provided routers worldwide might be running vulnerable firmware without anyone realizing it. https://quentinkaiser.be/security/2026/10/16/one-parser-two-bugs